Xenors AI Agents Guide • 2026
AI Agents for Cybersecurity in 2026: Defensive Uses, Limits and Risks
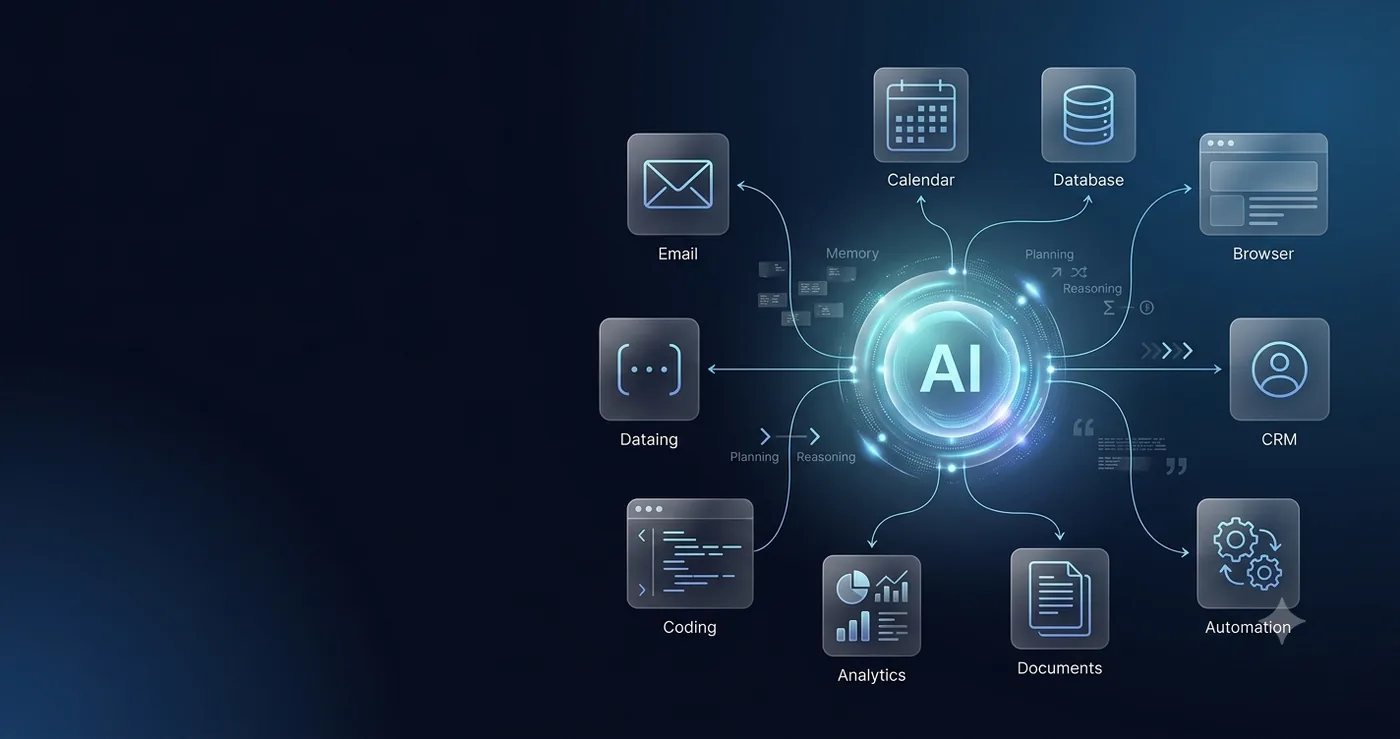
Cybersecurity agents can accelerate triage, enrichment and investigation, but powerful remediation actions require narrow permissions.
Cybersecurity agents can accelerate triage, enrichment and investigation, but powerful remediation actions require narrow permissions.
This guide is written for readers who want a usable explanation rather than a list of buzzwords. The focus is on real workflows, limits, evaluation and the practical decisions that make an AI system reliable.
How It Works in Practice
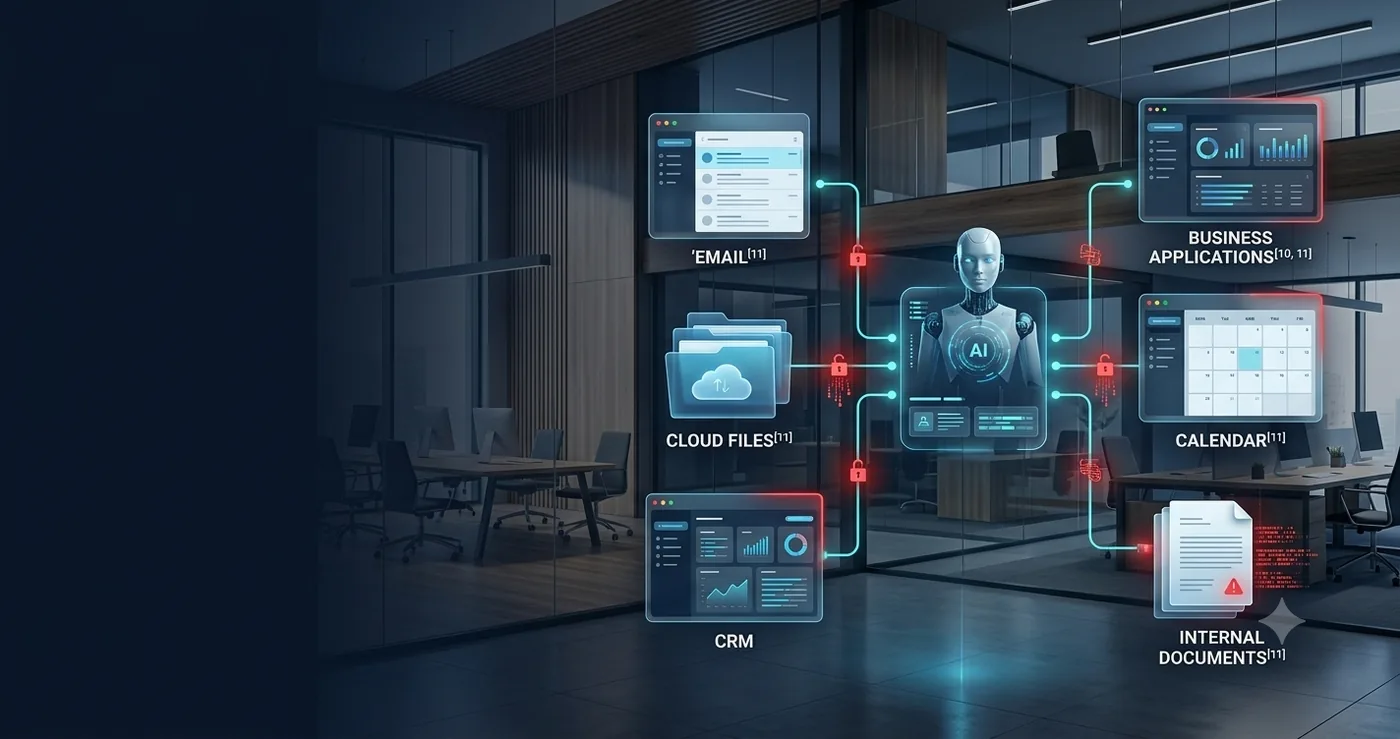
Security operations contain large volumes of alerts, logs and repetitive enrichment work. Agents can collect context, summarize evidence and recommend next actions.
Safe starting points include alert enrichment, phishing triage, vulnerability context, incident timelines, case documentation and playbook guidance.
Start with a workflow that a human team already understands. AI is easier to evaluate when the existing process has clear inputs, decisions and outcomes.
Where This Creates Real Value
High-impact remediation should use explicit thresholds and human approval because incorrect actions can disrupt operations.
Repetitive, measurable work with clear source data and reversible actions.
Vague processes, high-impact decisions with no verification path, or tasks that rarely repeat.
A Practical Implementation Plan
For AI agents for cybersecurity, implementation quality usually matters more than model hype. A useful pilot can be built around five stages.
- Define the outcome. Write one sentence describing what “done” means.
- Map required data. Separate trusted system data from unverified external content.
- Limit permissions. Give the workflow only the tools required for the task.
- Add checks. Validate outputs before high-impact actions.
- Measure and iterate. Compare the automated workflow with the previous baseline.
Risks and Failure Modes to Test
Common failures include missing context, stale data, duplicate actions, conflicting instructions, unavailable tools and overconfident outputs. Agent systems should be tested with deliberately difficult cases, not only clean demos.
For production use, keep logs or traces that show which information was used, which tools were called and why the workflow stopped or escalated. This makes errors easier to diagnose and creates accountability.
Frequently Asked Questions
What does AI agents for cybersecurity mean?
Cybersecurity agents can accelerate triage, enrichment and investigation, but powerful remediation actions require narrow permissions.
What is the safest way to start?
Start with a narrow, measurable, low-risk workflow. Use limited permissions, test edge cases and keep a human approval step for high-impact actions.
How should results be measured?
Measure task completion, correctness, human rework, latency, cost and error severity instead of relying on a demo or a single accuracy number.
Sources and Further Reading
Capabilities, frameworks and vendor limits evolve quickly. Verify product-specific pricing, permissions and data policies before deployment.